Matrix Store · Neo Audit
A production Next.js storefront seeded with real vulns, so Neo's audit engine could prove itself.
- Role
- Solo build (full-stack + DevOps)
- Year
- 2025
- Practice
- Software
- Link
- matrix.neo.audit
At a glance
- Starting point
- Develop a fully functional e-commerce application to showcase Neo's AI-powered security auditing capabilities, with real-world flows, observability, and secure deployment.
- What we built
- A production Next.js storefront seeded with real vulns, so Neo's audit engine could prove itself.
- Focus
- Security, Next.js, AWS
- Outcome
- Neo's automated security audit successfully detected all intentionally injected vulnerabilities and flagged additional edge-case issues.
A real e-commerce store, deliberately built to get hacked, so Neo's AI security audit could prove itself.
Goal
Develop a fully functional e-commerce application to showcase Neo's AI-powered security auditing capabilities, with real-world flows, observability, and secure deployment.
What I built
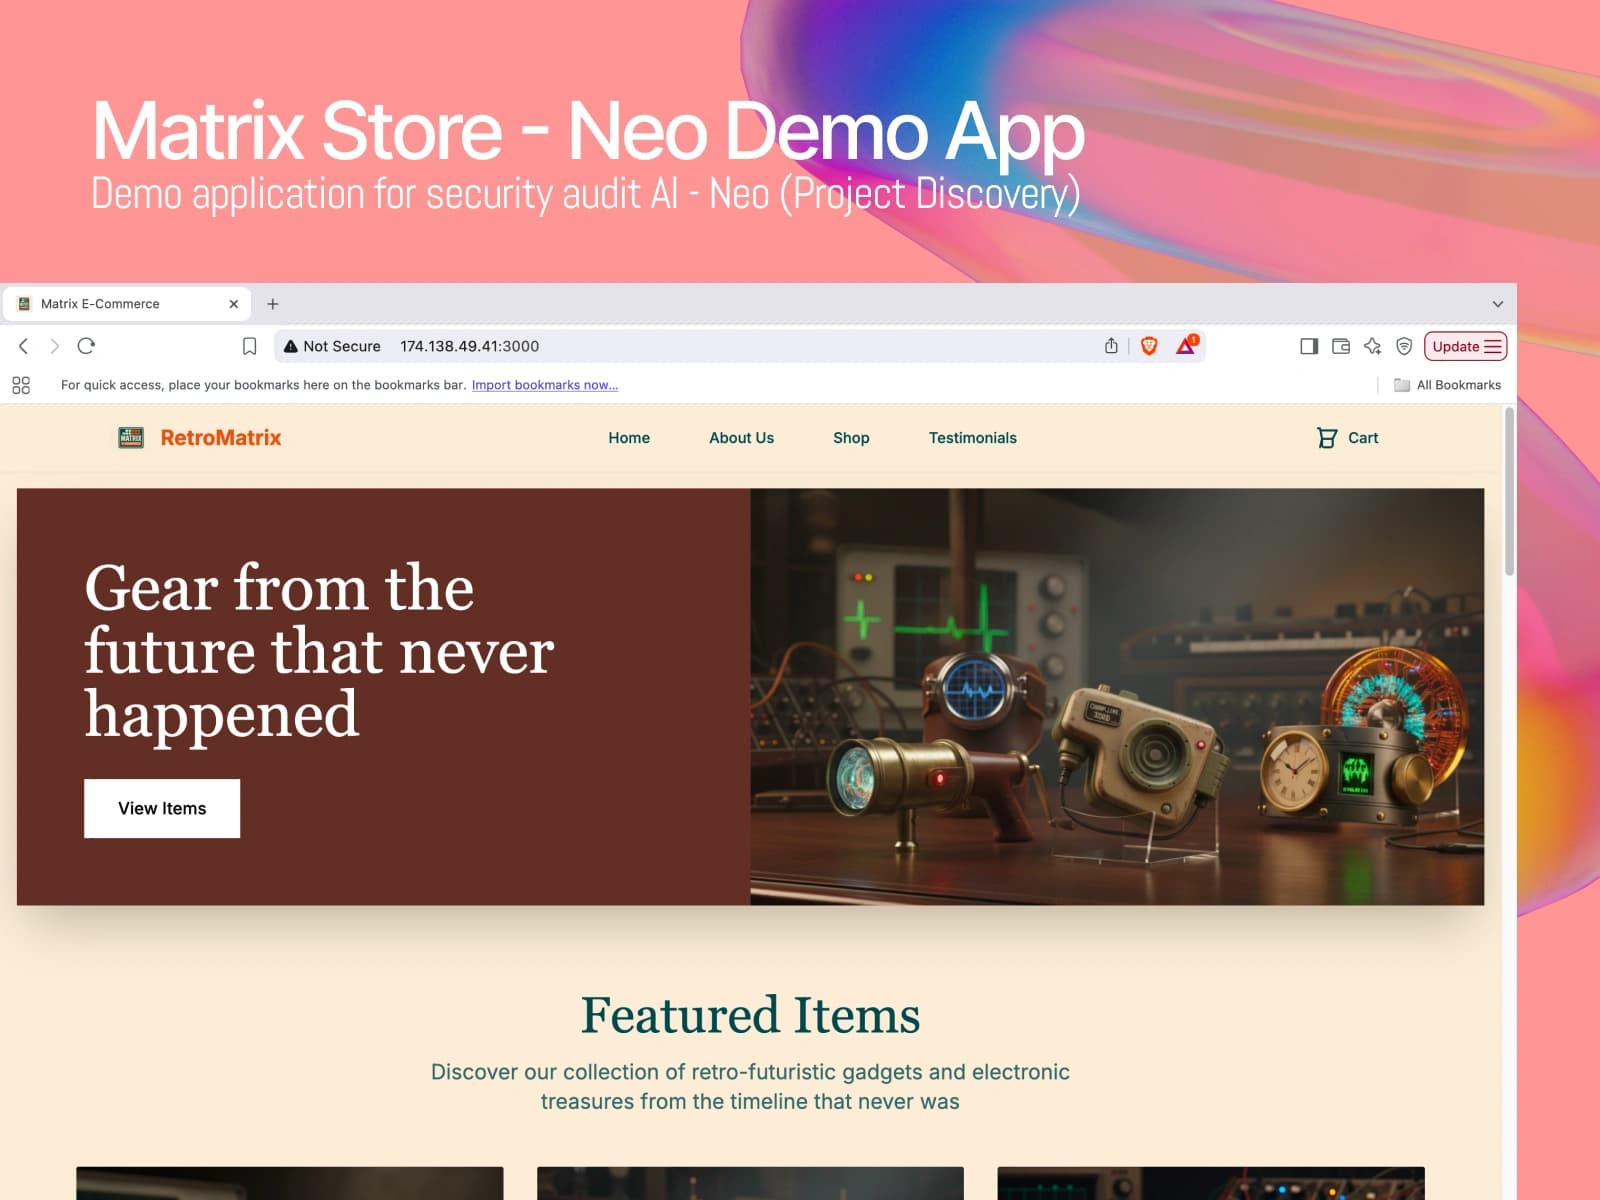
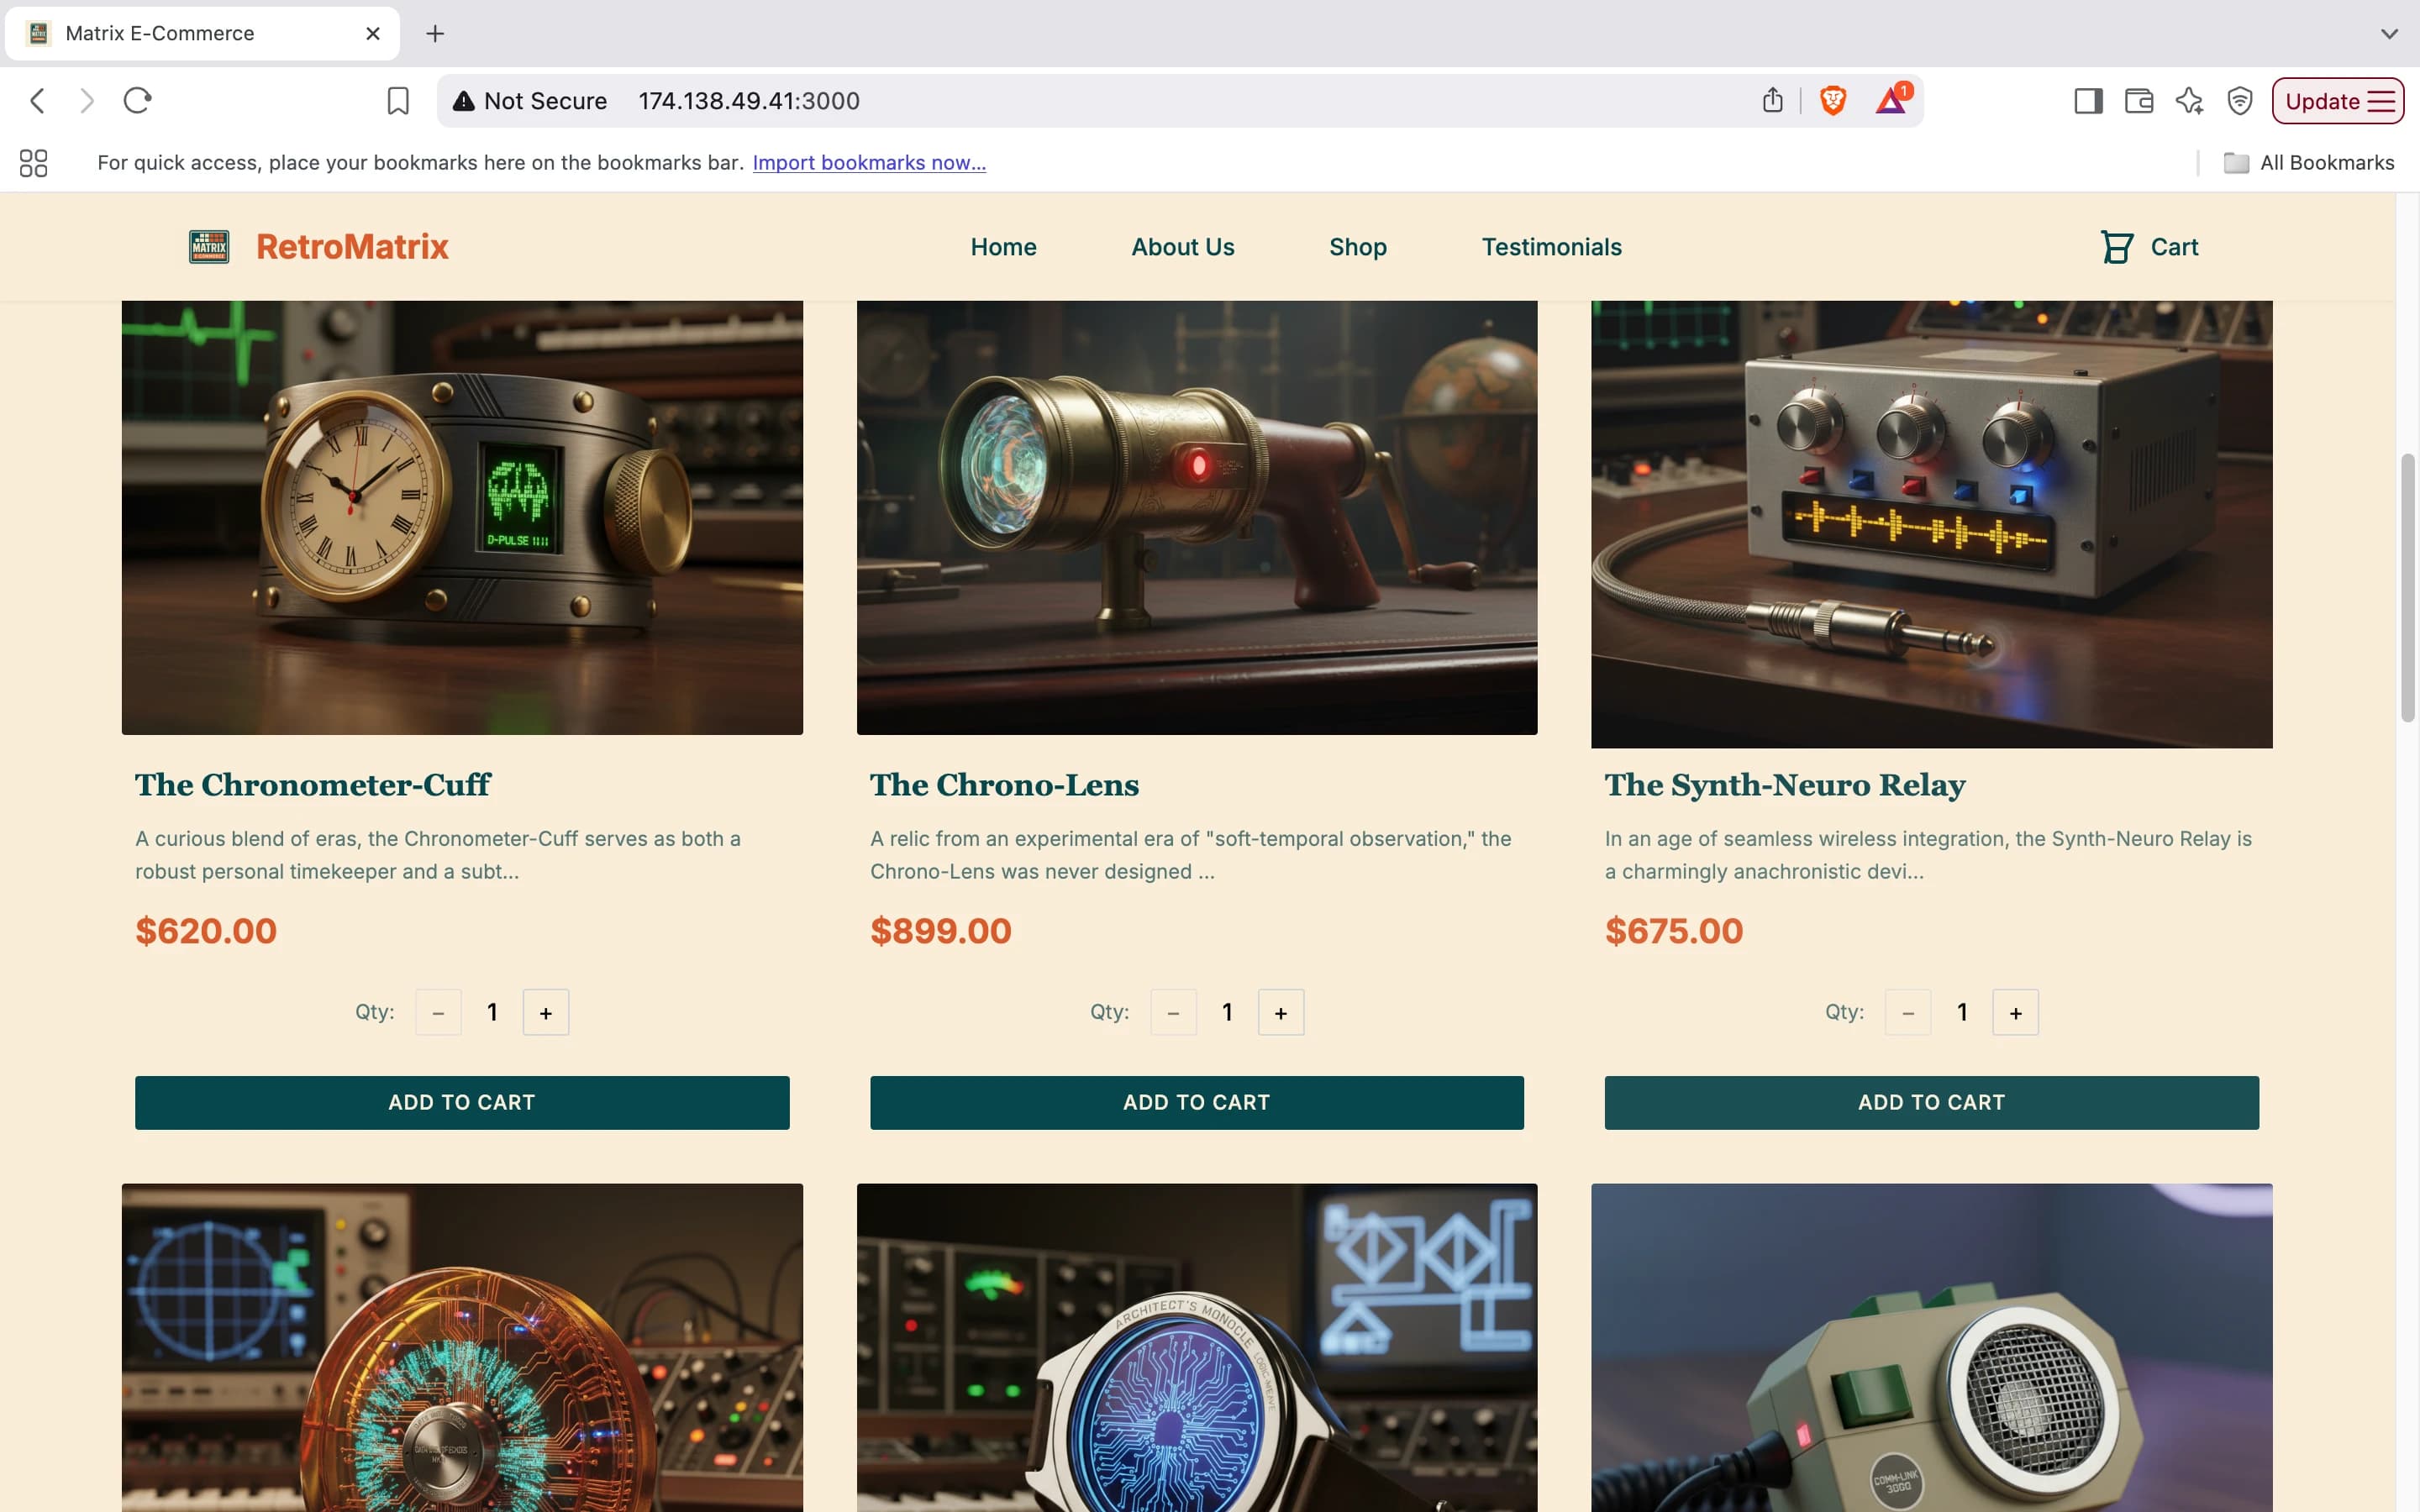
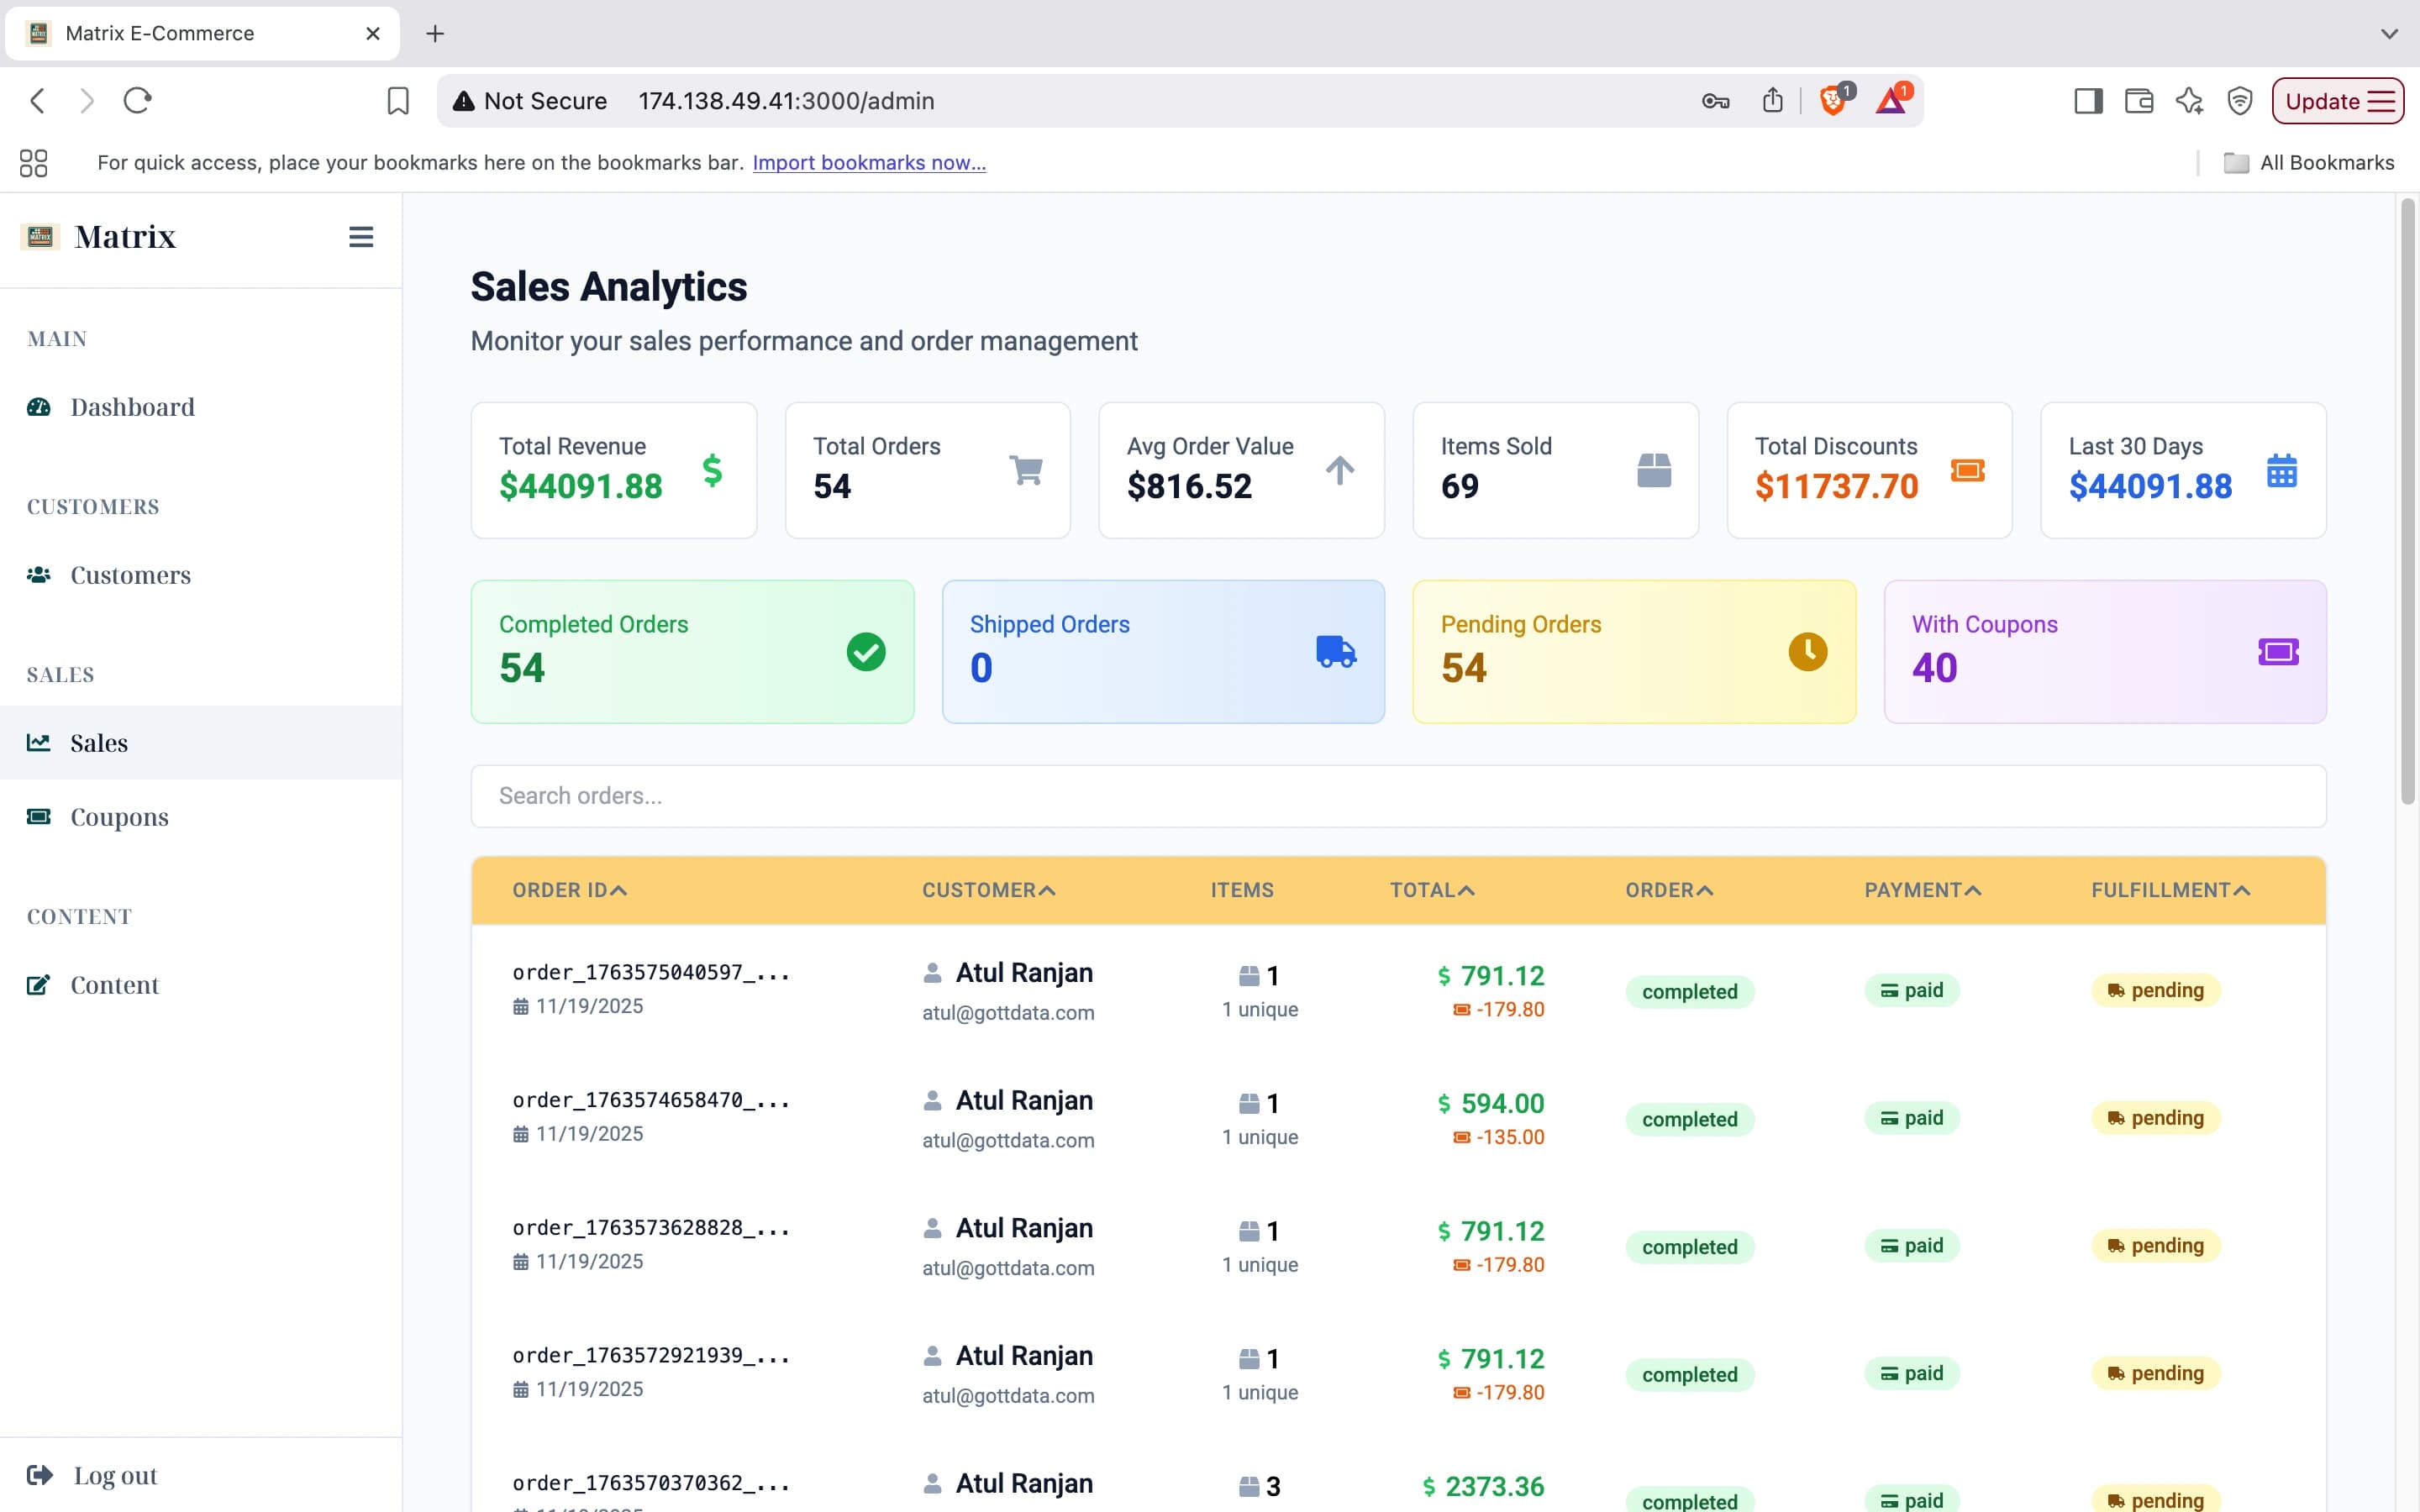
- Next.js (App Router) + TypeScript full-stack: products, cart, checkout, order placement, user dashboards.
- Firebase auth and seamless backend services.
- Realistic coupon system to surface business-logic and security edge cases.
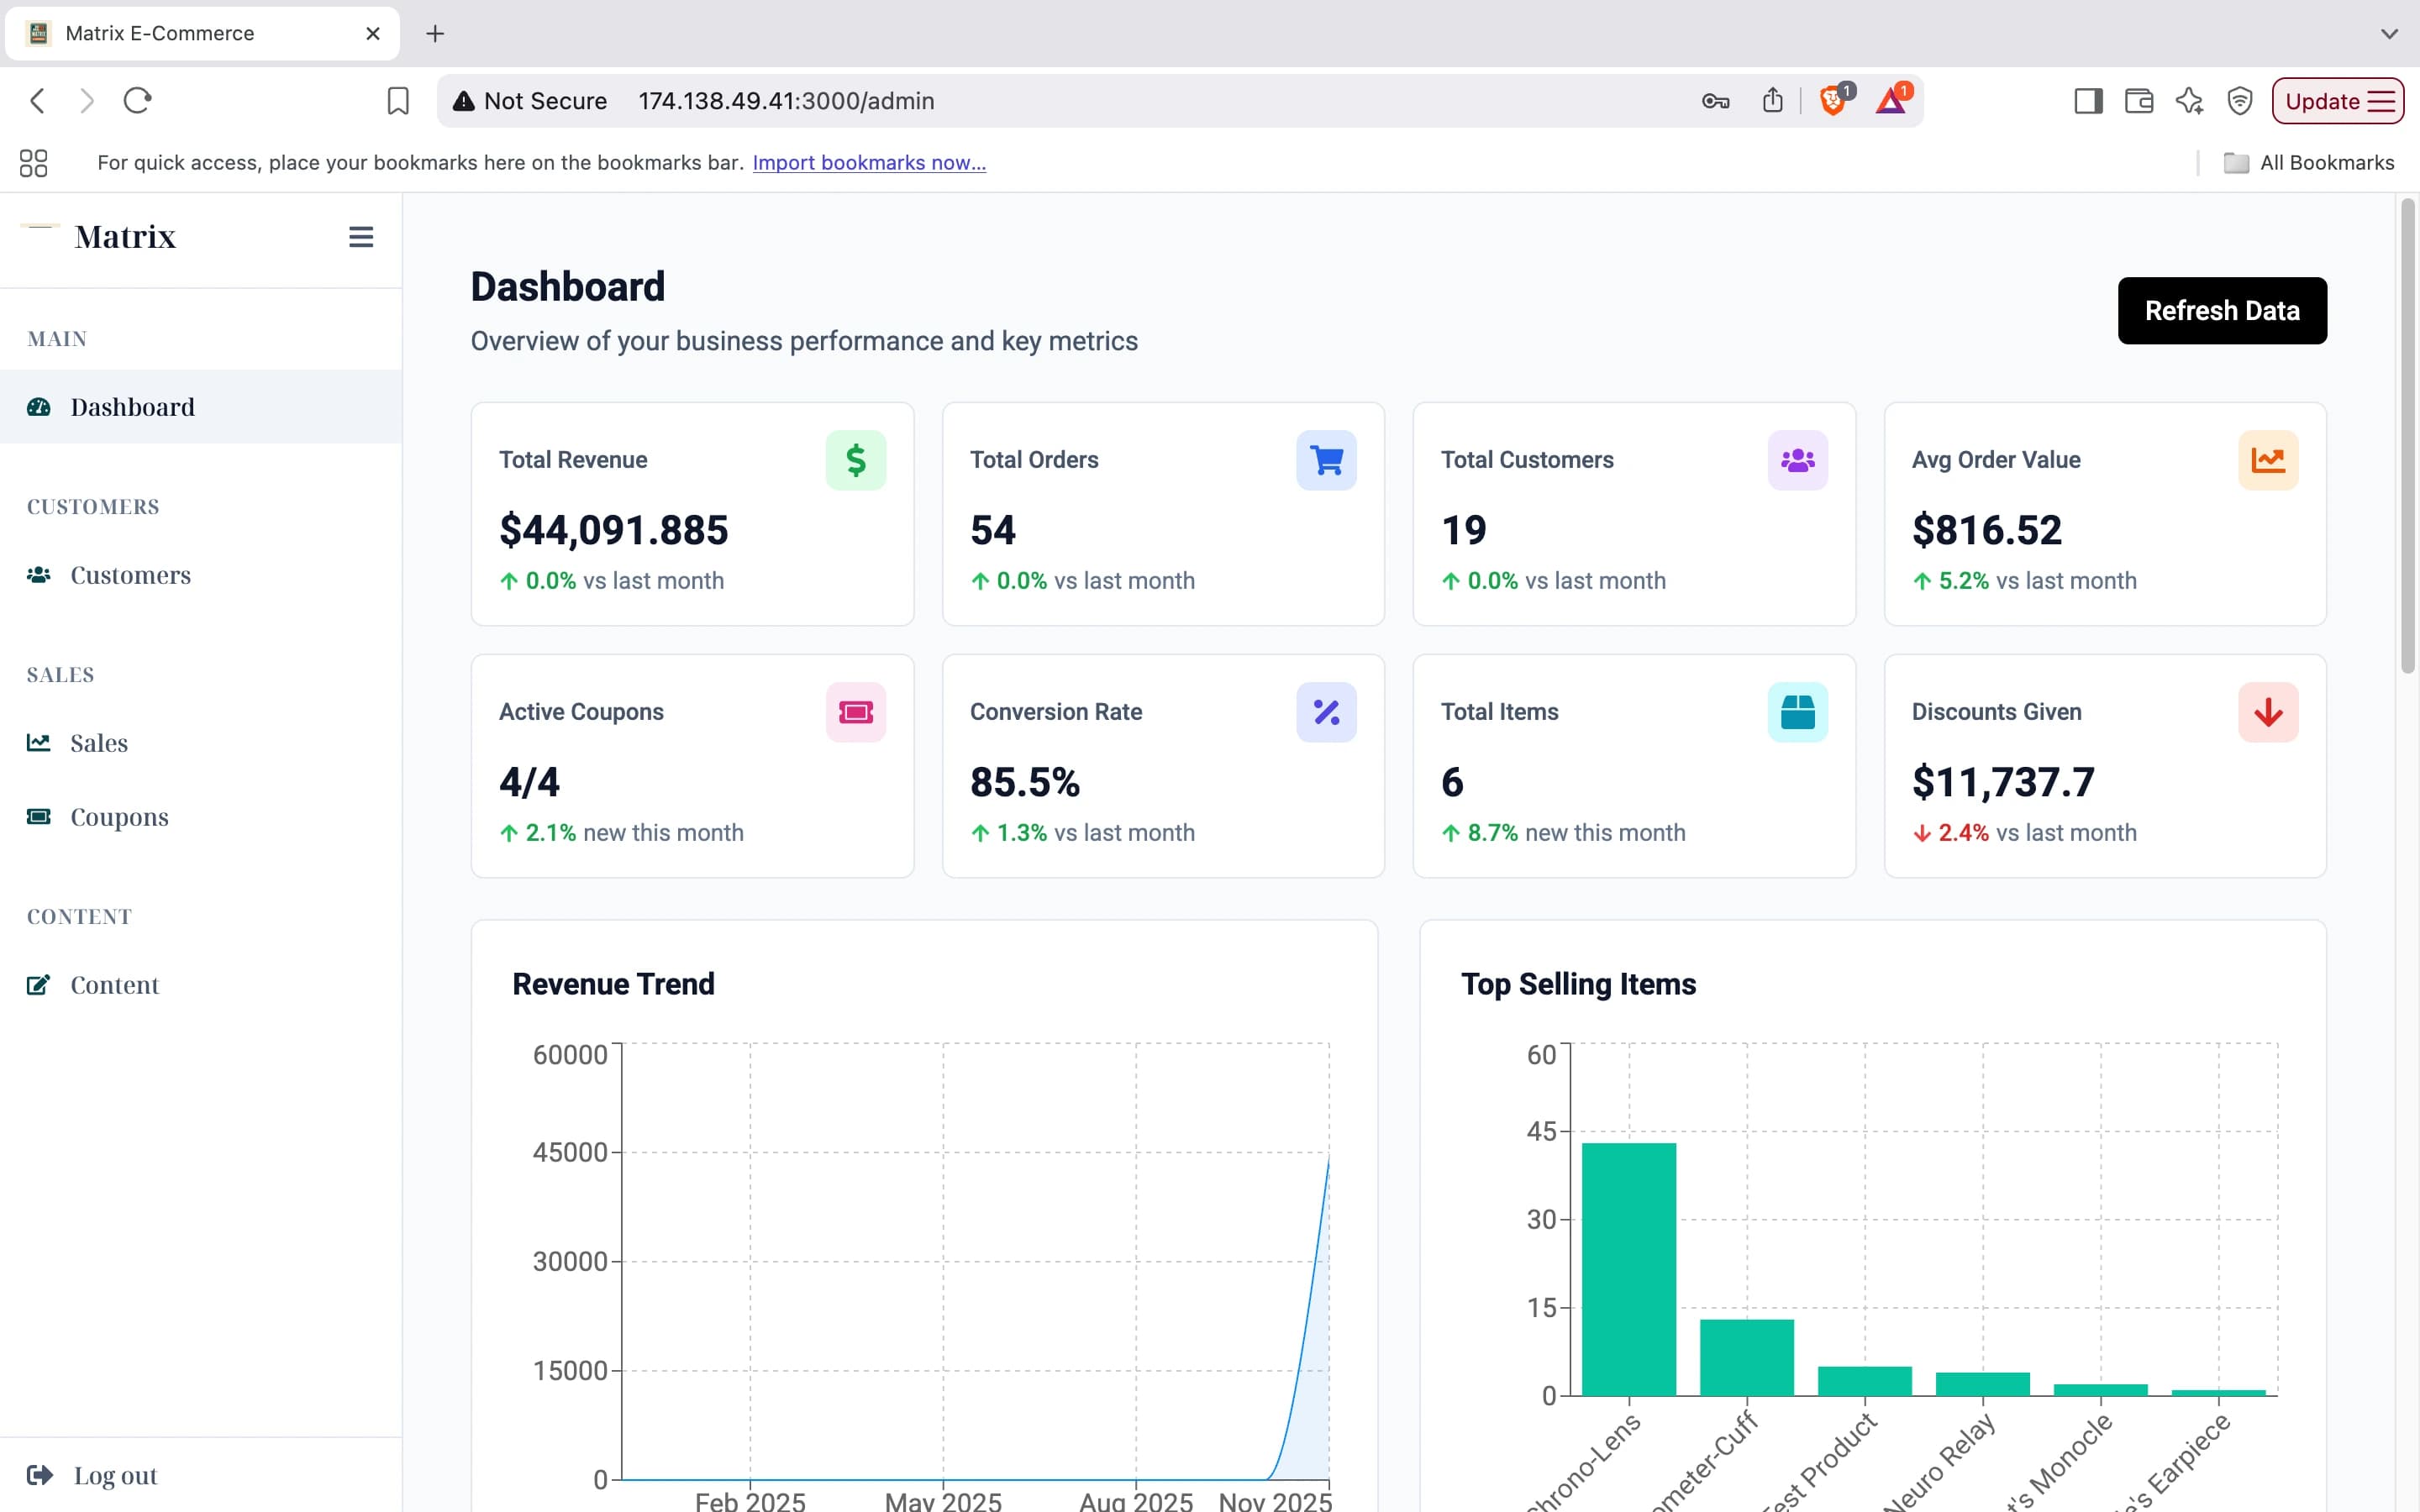
- Grafana dashboards monitoring API performance, coupon attempts, and security events.
- Containerized via Docker Compose; deployed to AWS with smooth CI/CD.
Security-first build
Applied OWASP standards, dependency hardening, secure auth flows, and API best practices. Considered every exploitation surface (coupon abuse, broken access control, input tampering, session flaws). Purposely left a small number of vulnerabilities for Neo's AI audit engine to find.
Outcome
Neo's automated security audit successfully detected all intentionally injected vulnerabilities and flagged additional edge-case issues. Patched and hardened, the site became a fully secure, production-ready demonstration of full-stack engineering, DevOps, and AI-driven security.